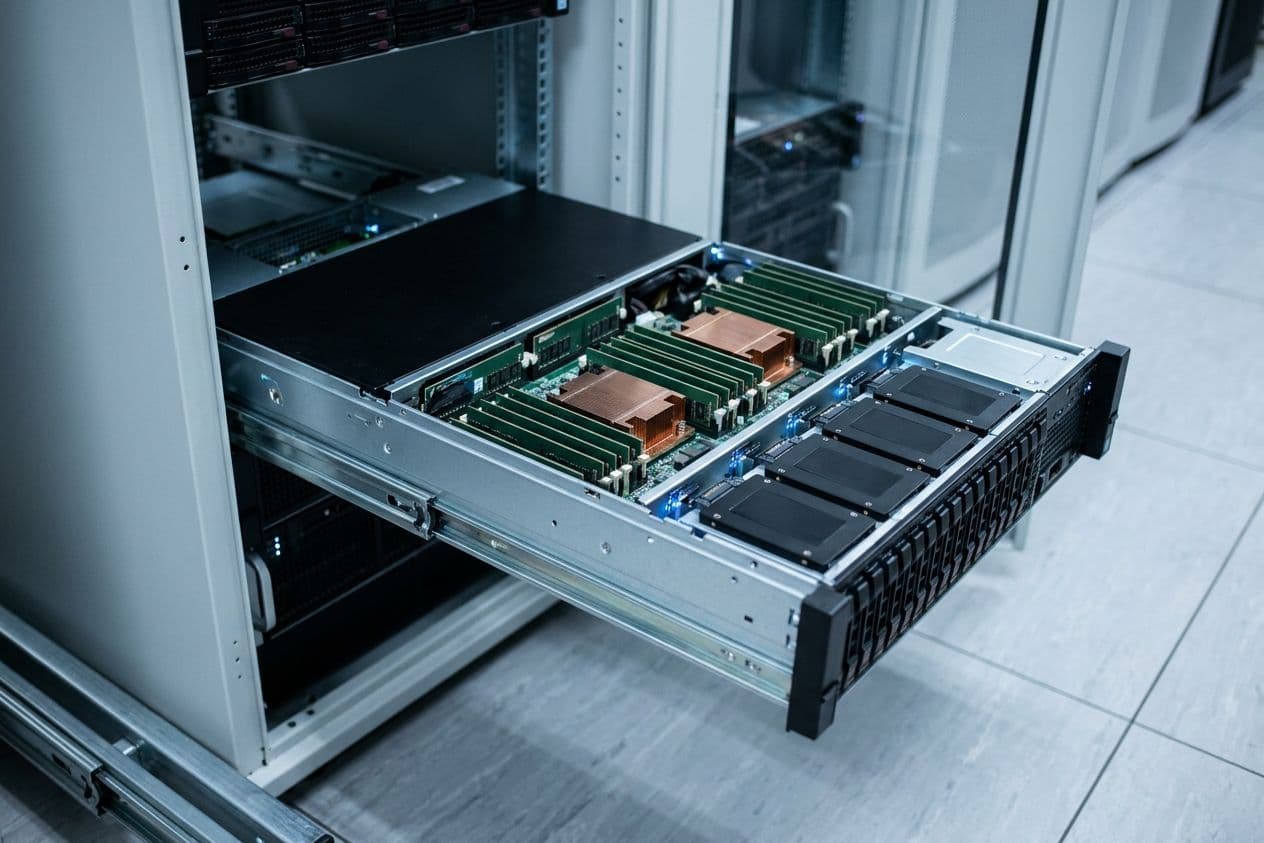
Real isolation, not a noisy neighbourhood
Every tenant gets its own network segment with its own firewall rule set, and isolation is enforced at layer two as well — a per-machine firewall does not see traffic between neighbours on the same bridge, so relying on it alone is a mistake we do not make.
- Separate network segment and rule set per tenant
- Layer-two separation in addition to per-machine filtering
- Guaranteed CPU and memory, NVMe-backed storage